This Design Scales Facial Verification by 10 Times
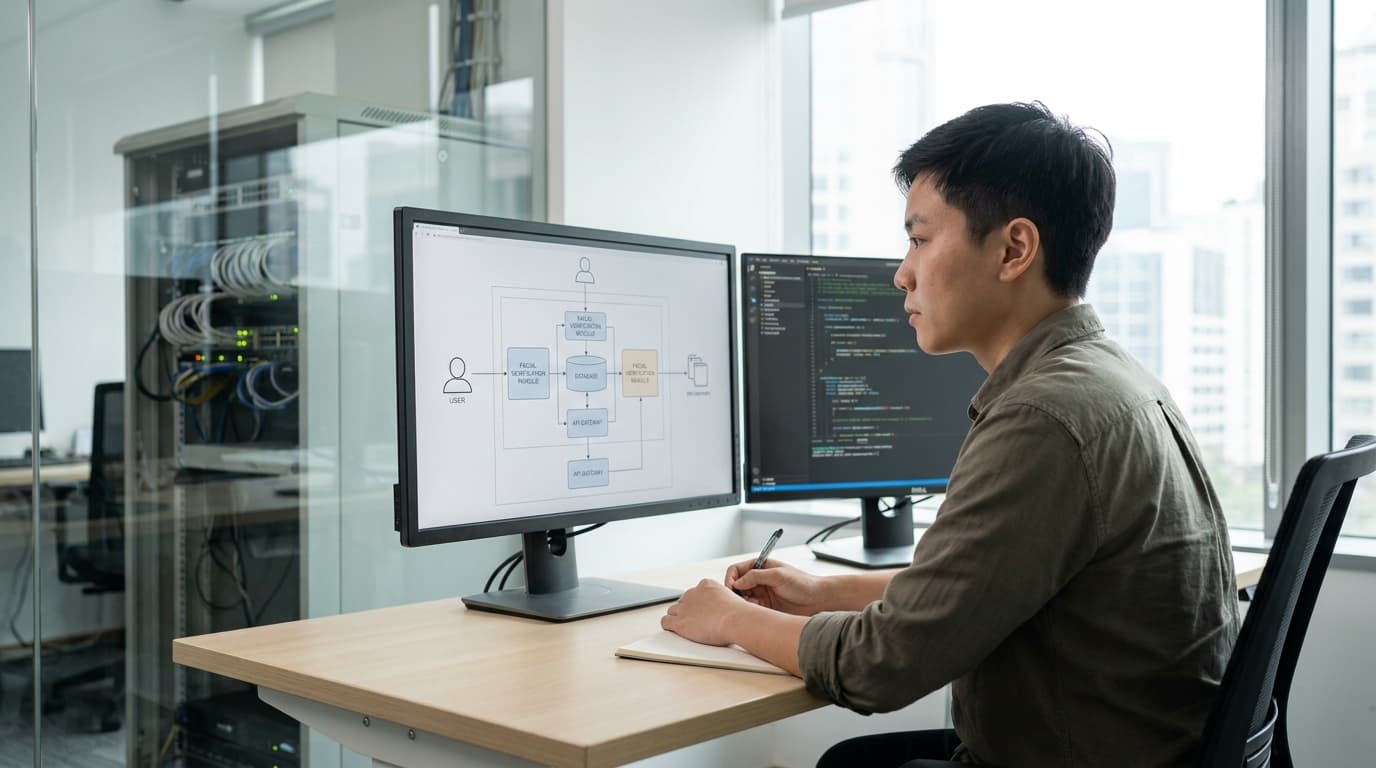
TL;DR: A new four-layer architecture for facial verification systems enables 10x scaling and cuts cloud costs by 30%. The design decouples key processes and adds privacy controls to meet GDPR and HIPAA compliance, even under heavy load.
Key facts
- Category
- Infrastructure
- Impact
- High
- Published
- Source
- InfoQ
Full summary
A new four-layer architecture enables facial verification systems to scale 10x while cutting cloud costs and ensuring GDPR and HIPAA compliance.
When thousands of users try to authenticate at once, many facial verification systems buckle under the strain. Traditional designs that rely on simple, synchronous API calls often fail, leading to outages and a poor user experience. An article from InfoQ by Praveen K presents a modern, four-layer architecture designed to solve this exact problem. The proposed model offers a blueprint for building facial verification systems that are not only highly scalable but also secure, cost-effective, and compliant with privacy regulations. By implementing this design, the author reports it is possible to achieve a tenfold increase in scaling capacity while simultaneously cutting cloud infrastructure costs by as much as 30%. This approach directly addresses the core challenges faced by companies deploying biometrics for large user bases, from enterprise workforces to consumer applications, providing a robust framework for reliability and growth.
The architecture's power comes from its four distinct, strategic layers. The first layer implements client-side filtering, which performs initial checks on the user's device before any data is sent to the cloud. This simple step weeds out poor-quality images or obvious mismatches locally, significantly reducing the volume of expensive cloud processing. The second layer decouples face detection from face verification. Instead of a single, monolithic service, these two tasks are separated, allowing the more computationally intensive verification process to be scaled independently to meet demand. The third layer introduces risk-based dynamic thresholds, which adjust the required confidence score for a match based on the context of the action, balancing tight security for sensitive operations with frictionless access for low-risk ones. Finally, the fourth layer is a zero-trust privacy framework that enforces explicit user consent and automates data purging, ensuring the system meets stringent compliance standards like GDPR and HIPAA by design, rather than as an afterthought.
This architectural pattern reflects a broader shift in how modern software systems are built. The move away from monolithic services toward decoupled, microservices-inspired designs is a well-established trend in cloud engineering, prized for its resilience and scalability. Applying this philosophy to facial verification addresses a critical industry need. As biometric authentication becomes increasingly common for everything from unlocking phones to corporate logins, the engineering challenge of doing so reliably and affordably at a massive scale has grown. Furthermore, this design directly confronts the growing tension between technology and privacy. By embedding consent gates and automated data deletion directly into the system's core, it embodies the principle of "privacy by design." This proactive approach is becoming essential as regulators and consumers alike demand greater control over sensitive biometric data, making compliance a foundational requirement, not just a feature to be added later.
For CTOs, security architects, and engineering teams, this four-layer model provides a practical and actionable blueprint for modernizing identity platforms. It encourages a critical evaluation of existing systems: Are we performing expensive computations in the cloud that could be offloaded to the client device? Is our system a single point of failure, or can its components scale independently? Is our approach to privacy and compliance built-in or bolted on? The principles outlined—client-side pre-processing, service decoupling, risk-based logic, and integrated privacy controls—offer a clear roadmap for building next-generation facial verification systems. Adopting this approach can help organizations create services that are more resilient, cost-efficient, and trustworthy, positioning them to handle future growth without compromising on security or regulatory obligations. It demonstrates that performance, cost, and privacy do not have to be trade-offs; with the right architecture, they can be mutually reinforcing.
Why it matters
For engineers building identity systems, this architecture offers a blueprint for avoiding common failure modes at scale. It shows how to handle massive concurrent requests without system collapse, a critical challenge for services like employee check-ins or large-scale user authentication.
Business impact
This architectural approach directly reduces operational costs by cutting cloud spending up to 30% and minimizes legal risk by baking in GDPR/HIPAA compliance. For companies deploying facial verification, it provides a competitive advantage by enabling reliable, high-volume services without ballooning infrastructure budgets.
Tags
Related on Notifire
Related stories
Primary source: InfoQ