Short, verified tech briefings on AI, Cybersecurity, Infrastructure, Database, and Tech Updates — with the analysis and action steps engineering teams need.
Microsoft is overhauling its Windows Insider Program, which provides early access to new Windows 11 features. The company is introducing significant changes, starting with giving testers the ability to select specific new features they want to try out, offering more control over their preview experience.
Cybersecurity researchers have identified four malicious packages on the npm registry: `chalk-tempalte`, `@deadcode09284814/axios-util`, `axois-utils`, and `color-style-utils`. These packages were designed to steal information from developer systems and have been downloaded thousands of times.
A new Linux Foundation report finds that security readiness is the biggest obstacle to AI adoption. A widening gap exists between the rush to deploy AI and the ability to secure it. The report notes 67% of teams face pressure to accelerate deployment despite security risks.
A newly analyzed computer virus from over 20 years ago, named fast16.sys, reveals an early Stuxnet-style attack. The malware was designed to selectively target high-precision calculation software, subtly altering results in memory. This highlights a long-standing threat of data manipulation in critical systems.
Actor Matt Ryan, who voices Edward Kenway, has confirmed he filmed new scenes for the upcoming Assassin's Creed Black Flag remake. The new content is intended to add more emotional weight and depth to the main character's personal conflicts and overall journey in the popular game.
Cloudflare is testing a new post-quantum system to restrict data by location. While it protects against future threats, its strict security-first design could risk causing regional outages if verification checks fail.
OpenBSD 8.0 has been released, bringing major updates for modern hardware and security. The new version adds support for Intel Arc graphics and improves virtualization, making the secure operating system more versatile for today's infrastructure.
A fake cryptocurrency trading app on Apple's App Store stole over $23,000 from users. The incident shows even tightly controlled ecosystems are vulnerable, posing a significant risk for teams relying on platform-level trust.
Fortanix now lets Kubernetes AI workloads prove they are secure before getting the keys to decrypt sensitive data. This integration with Confidential Containers offers a new way to protect valuable models and information while they are in use.
A crypto-mining campaign has returned to Hugging Face, hiding malware in AI models to hijack GPU servers. One malicious model was downloaded over 28,000 times, highlighting a persistent threat to the AI development community.
Prediction market Polymarket paused trading after a compromised third-party service injected malicious code. The script drained approximately $2.5 million from user wallets, highlighting the risks of relying on external dependencies for web applications.
A critical security flaw in the PostgreSQL extension E-Maj allows users to gain superuser privileges. The vulnerability affects all previous versions, and developers are urging an immediate update to version 5.0.1 to patch the issue.
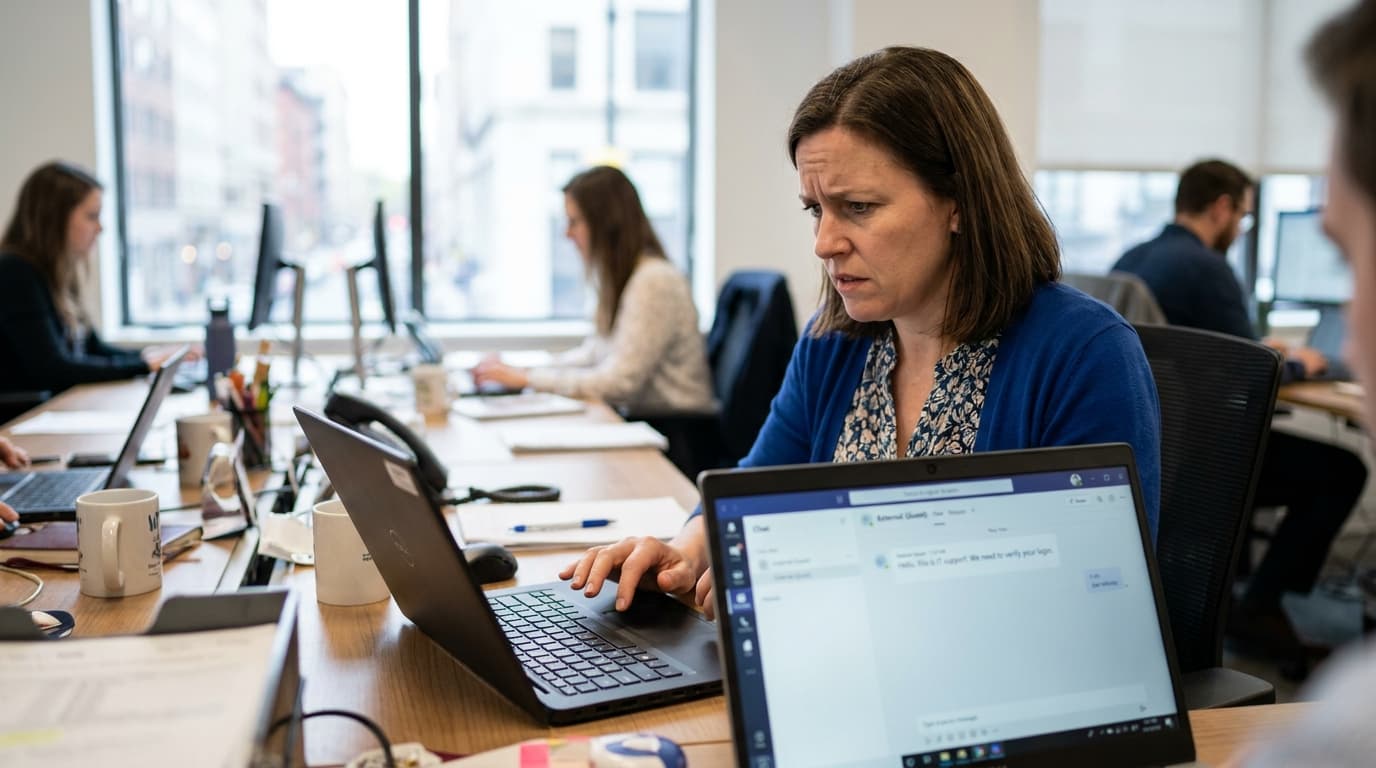
Attackers are exploiting a Microsoft Teams feature to send messages from outside your organization, posing as IT support. They trick employees into running malicious files, leading to malware and ransomware infections.
A state-sponsored hacking group called Volt Typhoon is using a new method, 'Silent Train,' to launch attacks. They create temporary chains of hijacked devices to hide their tracks, making them incredibly difficult to detect and block.
Microsoft reports North Korean hackers are using large language models to improve their cyberattacks. This allows them to craft more convincing phishing emails, research targets, and write malicious code, making them a more sophisticated threat.
Attackers are using AI agents to accelerate post-breach activities. After exploiting a PHP flaw to target a European government, an AI helped steal password hashes and multi-factor authentication data in under two hours, signaling a major shift in cyberattack speed.
Japan's GMO Group told customers to shut down their systems after a hacker breached its cloud service and threatened a ransomware attack. The extreme measure highlights the severity of the threat to its infrastructure.
Cisco has patched a critical zero-day vulnerability in its ASA and FTD firewalls. Attackers were actively exploiting the flaw to remotely crash devices, disrupting SSL VPN services and forcing reboots. Updates are available now.
OpenKruise Agents, a CNCF project, just released an update to help teams safely run AI agents on Kubernetes. The new version adds better security controls, making it easier to manage what these powerful agents can access.
A new report from Huntress shows attackers are increasingly using legitimate IT tools and Microsoft 365 to compromise businesses. This "living off the land" approach bypasses traditional defenses, forcing teams to focus on detecting unusual behavior.
A new Android spyware kit called uCreator is available for rent, letting attackers clone WeChat accounts and steal Telegram 2FA codes. It works by tricking users into installing tampered versions of the official apps from outside app stores.
OpenAI's chief scientist warns that AI is advancing so quickly our current safety methods may soon fail. He says AI will increasingly improve itself, leaving less time for essential human oversight and control.
Scammers are now using AI to create fake profiles, write convincing messages, and manipulate targets in romance scams. This makes it easier to scale deception and harder for victims to spot the fraud, posing new security challenges.
An automated attack is using stolen GitHub tokens to print your repository secrets into Actions logs. Attackers then download these logs to steal sensitive data from private and enterprise codebases, creating a significant new security risk.