Muse Used Your Brainwaves to Train Its AI
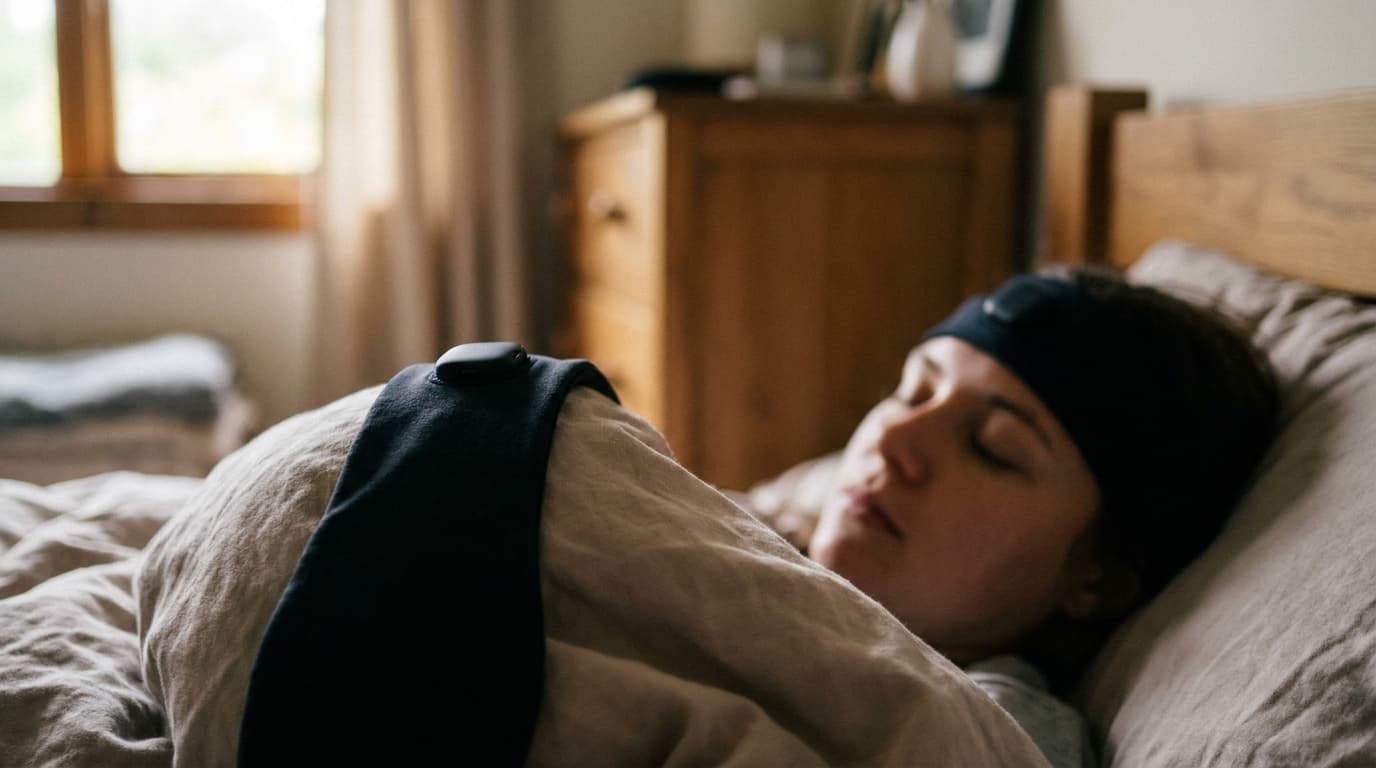
TL;DR: The company behind the Muse sleep headband used customers' brainwave data to train its AI models. The practice, done without explicit user consent, highlights growing privacy risks for sensitive biometric information in the age of AI.
Key facts
- Category
- Cybersecurity
- Impact
- High
- Published
- Source
- Malwarebytes Labs
Full summary
The maker of the Muse sleep headband used customer brainwave data to train AI, raising serious questions about consent and biometric data privacy.
Muse, the company behind popular EEG headbands for meditation and sleep tracking, used its customers' brainwave data to train artificial intelligence models. According to reporting from Malwarebytes Labs, this was done without obtaining clear and explicit consent from users for this specific purpose. People who purchased the devices were largely unaware that their highly sensitive biometric data was being repurposed for AI development. The data, collected to provide users with feedback on their sleep and meditation sessions, became a valuable training asset for the company. This practice highlights a critical and often-opaque aspect of modern tech products: personal data collected for one function is frequently used for another, especially to fuel the development of proprietary AI systems.
The core of the issue lies in the unique nature of the data itself. EEG (electroencephalogram) data is a direct measurement of the brain's electrical activity, creating a rich and distinctive neural fingerprint for each individual. While companies often claim such data is “anonymized” before being used in aggregate, research has repeatedly shown that complex biometric datasets are notoriously difficult to truly anonymize. Machine learning models can often re-identify individuals from supposedly anonymous EEG recordings by recognizing their unique brainwave patterns. This technical reality challenges the very concept of anonymization for such intimate data, meaning corporate promises of privacy may provide a false sense of security. The risk is not just a theoretical violation but the potential exposure of the most personal data a person can generate, revealing information about their cognitive and emotional states.
This incident is not an isolated event but part of a broader industry trend where user data is the primary fuel for AI innovation, often with murky consent frameworks. We have seen similar controversies arise from smart speakers using voice recordings, photo services using personal images, and chatbots using user conversations to train their models. What sets the Muse case apart is the unprecedented intimacy of the data. As more consumer health and wellness devices—from smart rings to continuous glucose monitors—enter the mainstream, the volume of sensitive biometric data being collected is exploding. Companies are strongly incentivized to leverage this data to improve their algorithms and gain a competitive edge, creating a fundamental tension between product development and user privacy. This case serves as a critical example of that tension reaching a new frontier.
For founders, developers, and security teams, the Muse story is a stark warning about the paramount importance of transparent data policies and explicit, granular user consent. Burying broad data usage clauses within a lengthy privacy policy is no longer a viable or ethical strategy, particularly when dealing with sensitive information like biometric data. Security leaders must now treat the re-identification risk of “anonymized” datasets as a genuine threat vector, not a theoretical problem. Looking ahead, regulations like GDPR and new AI-specific laws will almost certainly impose stricter controls on how this type of data is collected, stored, and used for model training. Companies that proactively adopt a privacy-first approach by offering users clear choices will not only mitigate legal and financial risk but also build the essential user trust needed to succeed.
Why it matters
This case demonstrates that even 'anonymized' biometric data like brainwaves can be a significant privacy risk due to re-identification potential. For engineering and security teams, it highlights the urgent need to re-evaluate data handling policies and the technical feasibility of true anonymization for complex biological datasets used in AI.
Business impact
Using customer data for AI training without explicit consent creates significant legal and reputational risk, potentially leading to costly fines and loss of user trust. Companies in the health and wellness tech space must now factor in stricter compliance and transparent data practices as a core part of their business strategy.
Tags
Related on Notifire
Related stories
Primary source: Malwarebytes Labs