That Microsoft Teams IT Request Might Be a Trap
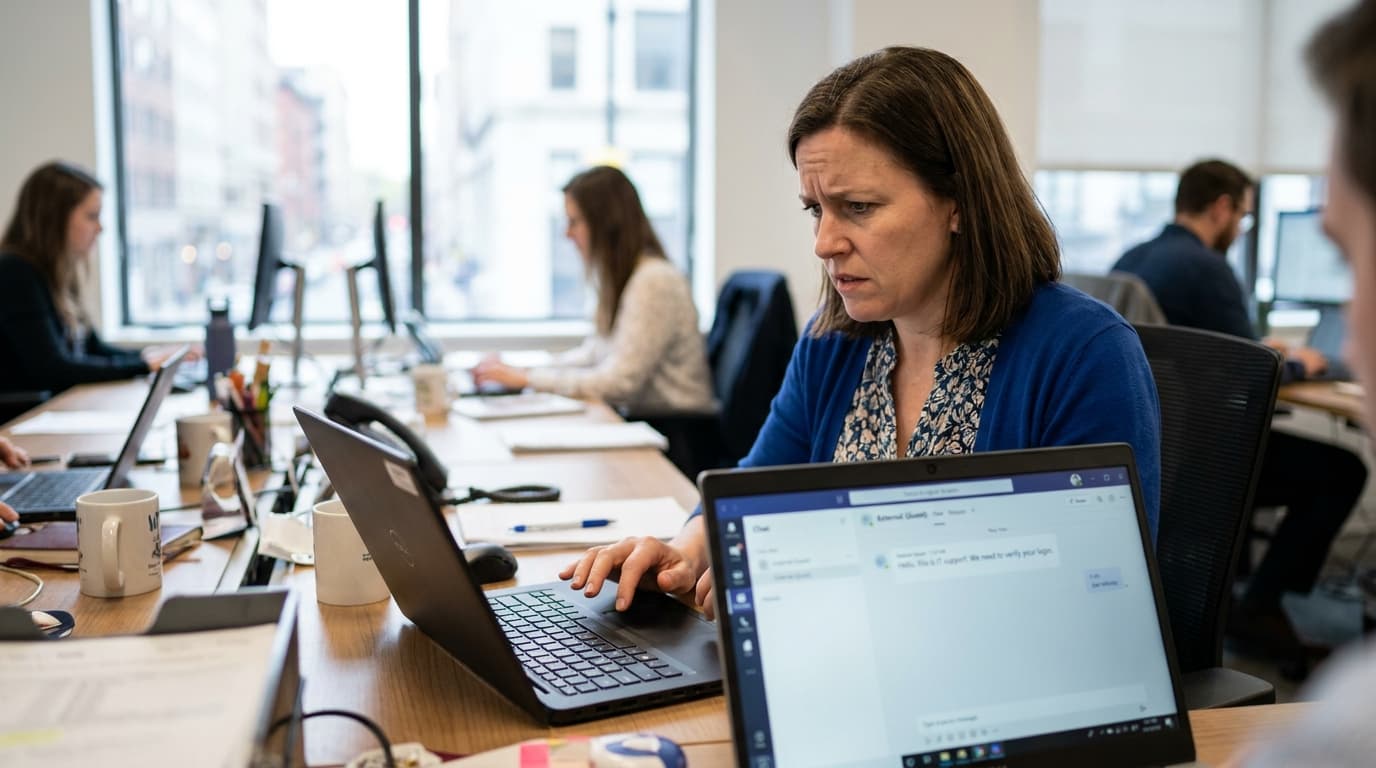
TL;DR: Attackers are exploiting a Microsoft Teams feature to send messages from outside your organization, posing as IT support. They trick employees into running malicious files, leading to malware and ransomware infections.
Key facts
- Category
- Cybersecurity
- Impact
- High
- Published
- Source
- The Hacker News
Full summary
Attackers are using Microsoft Teams to impersonate your company's IT support, tricking employees into installing malware and even deploying ransomware.
Cybersecurity researchers have identified a recurring social engineering campaign targeting Microsoft Teams users, according to a report from The Hacker News. Attackers are abusing the platform's external chat functionality to impersonate internal IT support staff. The goal of these impersonation scams is to trick unsuspecting employees into downloading and executing malicious files, which ultimately leads to the deployment of malware and, in some cases, ransomware. This tactic has been observed across hundreds of incidents, indicating a widespread and persistent threat that leverages the trust employees place in their company's primary communication tools. The attackers have shown a consistent pattern, using disposable Microsoft 365 accounts to launch their attacks, making them difficult to block preemptively. This approach turns a feature designed for collaboration into a potent vector for initial access into corporate networks.
The attack mechanism is simple but effective, preying on basic human trust. It begins when an attacker, using an account from an external Microsoft 365 tenant, initiates a chat request with an employee inside the target organization. By default, Microsoft Teams allows users to receive messages from external accounts, often flagging them with a simple "External" label that can be easily overlooked. The attacker customizes their profile name to something generic and plausible, such as "IT Support" or "Helpdesk," to appear legitimate. They then engage the employee with an urgent-sounding request, claiming a critical security update is needed or a system issue requires a troubleshooting script to be run. The user is directed to download and execute a file, which is disguised as a helpful tool but is in fact a malicious payload. This payload can be anything from a remote access trojan that gives the attacker a foothold in the network to a full-blown ransomware encryptor.
This campaign is a modern adaptation of a classic social engineering playbook, shifting the attack surface from email to collaboration platforms. For years, security teams have focused on filtering malicious emails and training users to spot phishing attempts. However, attackers are now migrating to tools like Microsoft Teams, Slack, and Discord, which are often perceived by employees as safer, walled-garden environments. This misplaced sense of security makes users more susceptible to manipulation. The rise of remote and hybrid work models further complicates the situation, as employees can no longer simply walk over to the IT department to verify a suspicious request. This attack highlights a broader trend where threat actors exploit the default, often permissive, configurations of enterprise software-as-a-service (SaaS) platforms. They are not breaking through complex technical defenses but are simply walking through a door that was left unlocked.
The primary defense against this threat is a combination of technical controls and continuous user education. Security and IT teams should immediately review their organization's Microsoft Teams federation settings, which control communication with external tenants. If cross-organization collaboration is not a business necessity, disabling external access entirely is the most secure option. Alternatively, organizations can create an allowlist of trusted external domains while blocking all others by default. Alongside these technical measures, it is crucial to train employees to be vigilant. They must be taught to recognize the "External" user label in Teams, to be inherently skeptical of unsolicited requests for action, and to never run executables sent via chat. A clear protocol for verifying the identity of IT staff, such as through a separate, known communication channel, should be established and reinforced. As attackers continue to innovate, security strategies must evolve to cover these increasingly popular collaboration vectors.
Why it matters
This attack vector bypasses traditional email security gateways by using a trusted enterprise collaboration platform. It highlights a critical configuration risk in Microsoft Teams' default settings that allows unsolicited external communication, creating a direct path for social engineering and malware delivery into corporate networks.
Business impact
A successful attack can lead to widespread ransomware deployment, causing significant operational downtime, data loss, and financial costs from recovery efforts. The reputational damage and erosion of trust in internal communication channels can also have long-lasting negative effects on the organization.
⚡ Action needed
Review and update Microsoft Teams external access policies to mitigate this threat.
Action checklist
- 1Review your Microsoft Teams external access settings. Consider blocking all external domains by default and using an allowlist for trusted partners.
- 2Train employees to identify and report suspicious Teams messages, especially those from users marked as "External."
- 3Instruct users to never download or run files sent by unverified contacts, even if they claim to be from IT.
- 4Establish a clear, out-of-band verification process for any unsolicited IT support requests, such as calling the help desk directly.
- 5Implement security monitoring to detect and alert on unusual Teams activity, such as a spike in new external communications.
Tags
Related on Notifire
Related stories
Primary source: The Hacker News