Apple Patches Exploited Flaw on Older iPhones
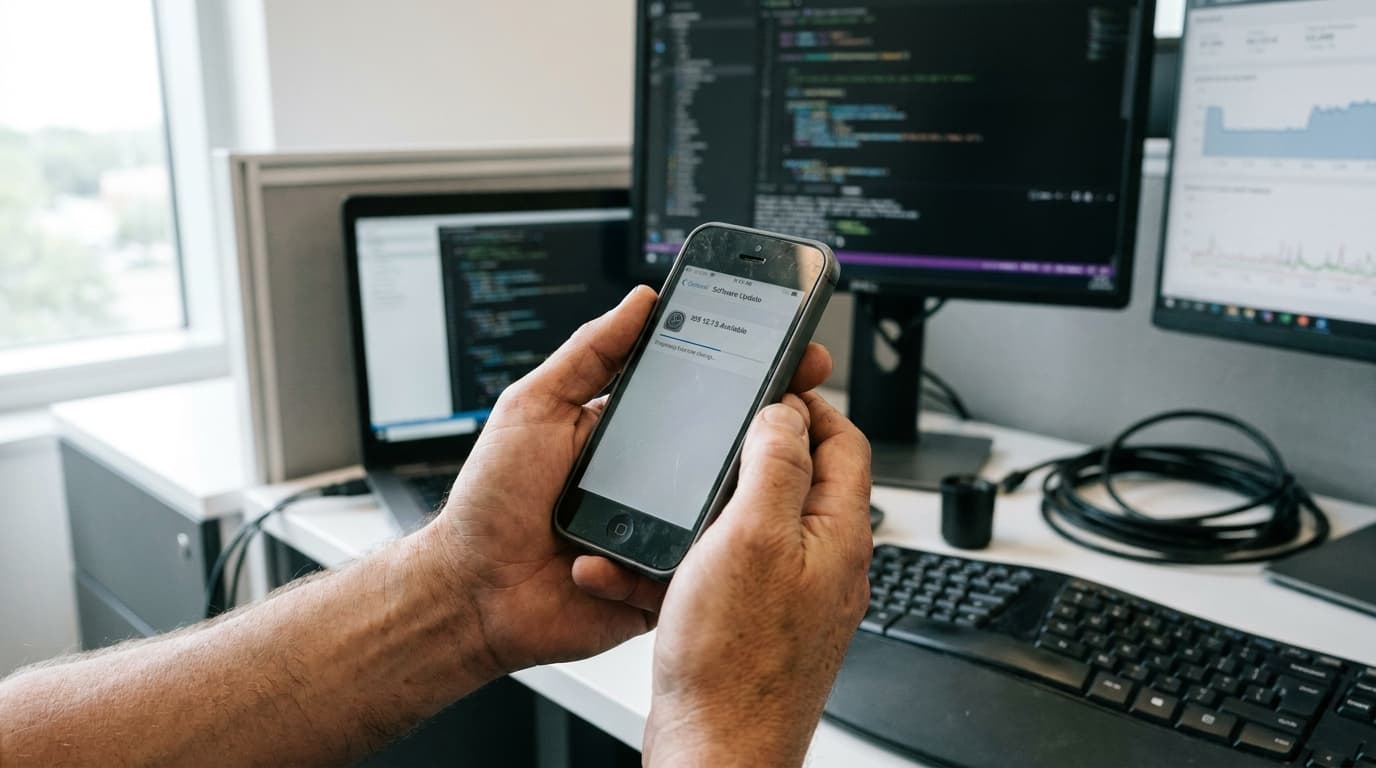
TL;DR: Apple has released an emergency security update for older iPhones and iPads. The patch fixes a critical flaw that attackers are already using to execute malicious code on unpatched devices that can no longer get the latest iOS.
Key facts
- Category
- Cybersecurity
- Impact
- Critical
- Published
- Source
- The Hacker News
Full summary
Apple released an emergency patch for a critical flaw on older iPhones and iPads that attackers are already actively exploiting in the wild.
Apple has issued an urgent security update for older iPhones and iPads, addressing a high-severity vulnerability that the company confirmed is being actively exploited. The patch was backported to devices that are no longer eligible for the latest major operating system releases, such as iOS 17. This move underscores the critical nature of the flaw and the ongoing risk that legacy hardware poses within both consumer and enterprise environments. The vulnerability, rated 8.8 on the CVSS severity scale, could allow an attacker to take control of a device simply by tricking a user into opening a specially crafted file. Given that attackers are already using this exploit in the wild, the update is not a routine maintenance release but an emergency response to an immediate threat.
At its core, the vulnerability is an out-of-bounds write issue within CoreGraphics, Apple's foundational framework for 2D graphics rendering. CoreGraphics is responsible for drawing nearly everything on the screen, from application interfaces to images and PDF documents. An out-of-bounds write is a classic memory corruption bug where a program writes data past the boundary of its intended memory buffer. In this case, a malicious file could be crafted to exploit this behavior when processed by CoreGraphics. This memory corruption can be leveraged by an attacker to achieve arbitrary code execution, granting them the ability to run any command on the affected device. This effectively hands over control to the attacker, enabling them to steal data, install malware, or spy on the user.
This incident highlights two significant trends in the cybersecurity landscape: the importance of backporting security fixes and the persistent targeting of low-level, memory-unsafe code. By providing patches for older devices, Apple acknowledges that millions of these products remain in active use and are part of the broader ecosystem that needs protection. For businesses, this is a critical service, as corporate device fleets often include a mix of new and aging hardware. The vulnerability's location in CoreGraphics is also telling. Graphics and media processing libraries are a common target for attackers because they are complex, often written in languages like C and C++, and are constantly required to parse untrusted data from external sources. This combination creates a fertile ground for memory-related bugs that can be turned into powerful exploits.
For CTOs, IT managers, and security teams, the key takeaway is that a device's age does not diminish its potential as a security liability. In fact, older devices often represent a weaker link in an organization's defenses. This patch serves as a critical reminder to maintain a comprehensive inventory of all assets, including legacy hardware, and to have a robust mobile device management (MDM) strategy capable of rapidly deploying emergency updates. Teams should not only prioritize the immediate installation of this patch but also review their device lifecycle policies. As attackers grow more sophisticated, relying on hardware that no longer receives full security support becomes an increasingly untenable risk. The next step is to prepare for similar zero-day events, as the time between a vulnerability's discovery and its active exploitation continues to shrink.
Why it matters
This backported patch addresses a zero-day vulnerability being actively exploited. For engineering and security teams, it's a reminder that legacy devices remain a significant attack surface. Failing to update these older assets can leave critical gaps in an organization's security posture, even if newer devices are patched.
Business impact
Unpatched older devices in a corporate fleet represent a major security risk. A successful exploit could lead to data breaches, unauthorized access to corporate networks, and significant reputational damage. This forces IT teams to dedicate resources to managing and updating a fragmented device ecosystem, increasing operational costs.
⚡ Action needed
Immediate patching is required for all affected older Apple devices. IT and security teams should prioritize deploying these updates across their device fleets to mitigate the risk of active exploitation.
Action checklist
- 1Identify all older iPhones and iPads in your device inventory.
- 2Deploy the latest available iOS and iPadOS updates for those models.
- 3Verify that the patches have been successfully applied across all devices.
- 4Communicate the urgency of this update to all end-users.
- 5Review device lifecycle policies to phase out unsupported hardware.
Tags
Related on Notifire
Related stories
Primary source: The Hacker News