One Request Can Hijack Your AI Gateway
A critical flaw in the Bifrost AI gateway lets attackers run any command without a password. This gives them full control over the server, exposing sensitive data and AI models.
60 verified briefings on Vulnerability. Each story includes a plain-English summary, why it matters, and the concrete action engineering teams should take.

A critical flaw in the Bifrost AI gateway lets attackers run any command without a password. This gives them full control over the server, exposing sensitive data and AI models.

The PostgreSQL team has released a critical security update for all supported versions, patching 28 vulnerabilities and over 110 bugs. This major release requires immediate attention from anyone running a PostgreSQL database to prevent potential exploits.

Researchers found critical security flaws in an open-source AI agent platform called Paperclip. The bugs could allow attackers to take over developer machines, exposing a fundamental trust issue in how AI agents are designed and deployed.

Researchers found a way to jailbreak vision-language AI models using tiny, invisible changes to images. This new attack method bypasses standard safety filters that only analyze text prompts, creating a significant new security risk.

A high-severity vulnerability has been discovered in the Geospatial Data Abstraction Library (GDAL). The flaw, located in its bundled LibTIFF component, could allow an attacker to execute arbitrary code, cause a denial of service, or access sensitive information by using a specially crafted TIFF image file.

Security researchers have detailed a method for interacting with and testing Windows kernel-mode drivers without the physical hardware they control. This approach simplifies vulnerability analysis, allowing security teams to evaluate driver exploits that are normally gated by the presence of specific hardware components.

Multiple vulnerabilities have been discovered in MediaWiki, the popular open-source wiki software. The flaws could allow attackers to determine if users have two-factor authentication enabled and to view the titles of intentionally hidden log entries, posing a risk to user privacy and site security.

The Crypt-SaltedHash library for Perl used a weak method to generate random "salts," a key part of password security. This makes the salts predictable, allowing attackers to more easily crack hashed passwords on systems using this library.

A vulnerability was discovered in Ubuntu's System Security Services Daemon (SSSD). A local attacker can exploit this by sending malformed data to the PAM passkey responder, causing it to crash. This results in a denial of service, preventing users from authenticating on affected systems.

A security flaw has been found in a core audio library on Ubuntu 20.04 LTS. Attackers could exploit it with a special file to crash applications or potentially run malicious code, requiring an immediate system update.

Ubuntu has released a security update for its 20.04 LTS version, addressing a vulnerability in the xdg-dbus-proxy component. The flaw could allow a local attacker to intercept certain D-Bus messages by exploiting incorrect handling of policy rules. Users are advised to apply the patch promptly.

A security vulnerability has been found in the NNCP file transfer utility. The flaw allows a remote attacker to bypass directory restrictions and read or write files anywhere on the system. This is a high-severity path traversal issue affecting users of this specific tool.
A security patch has been released for a critical GStreamer vulnerability affecting Ubuntu 16.04 LTS. Malicious AVI files could allow attackers to crash systems or run arbitrary code, making this update crucial for teams managing legacy infrastructure.

Elastic has released version 8.19.16 of the Elastic Stack, a security patch that addresses potential vulnerabilities. The company recommends all users upgrade to this latest version to ensure their deployments are protected. This update supersedes previous versions and is crucial for maintaining system security.

A remote code execution vulnerability was found in the Papers reference management app on Ubuntu. Attackers can exploit it by tricking users into opening a malicious PDF file, potentially allowing them to run arbitrary code. The flaw stems from how the application handles specific PDF actions.

A security flaw has been discovered in the Texmaker LaTeX editor. The vulnerability stems from how the application handles TIFF image files, allowing a malicious image to cause a denial of service, leak sensitive information, or permit remote code execution on a user's system.

Google issued an urgent update for a critical Chrome vulnerability that could allow code execution. Meanwhile, attackers are actively exploiting flaws in Microsoft Defender. Other security news includes scrutiny of child safety on major platforms and new spyware detection tools.

Ubuntu has patched a critical vulnerability in its GDK-PixBuf image library. A specially crafted JPEG file could crash an application, cause a denial of service, or even allow an attacker to execute arbitrary code on affected systems.

A security vulnerability has been discovered in the libcaca library. The flaw stems from incorrect handling of malformed files, which could allow an attacker to crash an application, causing a denial of service. In a worst-case scenario, this could lead to remote code execution.
A security vulnerability has been discovered in GStreamer Good Plugins. Specially crafted MP4 audio files can cause applications using the framework to crash, leading to a denial-of-service condition. This affects systems relying on GStreamer for multimedia processing. Users should apply available security updates.

Ubuntu has released a security update for its 18.04 LTS and 20.04 LTS versions. The patch addresses a denial-of-service vulnerability in the OpenCC library, which could be triggered by an attacker using specially crafted, truncated UTF-8 input to crash applications using the library.

A recent security bulletin highlights a range of emerging threats facing organizations. These include the misuse of AI agents for malicious purposes, the availability of new command-and-control tools for attackers, deceptive social engineering tactics, and the continued use of JavaScript backdoors to compromise systems.

A cross-site scripting (XSS) vulnerability was discovered in Postorius, the web interface for Mailman 3. The flaw allows attackers to inject malicious HTML into message subjects on the 'Held messages' pop-up, which could lead to the exposure of sensitive administrator information.
This week's security landscape saw several critical developments. A new vulnerability was discovered in the Linux kernel, while a significant exploit targeted Palo Alto Networks' PAN-OS. Additionally, the use of AI in crafting sophisticated attacks is on the rise, alongside new OAuth-based phishing campaigns.
A public exploit is now available for a recently patched Arch Linux vulnerability called PinTheft. The flaw allows a local attacker to gain full root privileges on a system. The vulnerability has already been fixed, so users who have updated their systems are protected from this exploit.

A security vulnerability has been discovered in libeconf, a configuration file parsing library used in Linux environments. The flaw could allow an attacker to cause a crash by sending improperly sized input, resulting in a denial of service. Ubuntu has issued a patch to address the issue.

Microsoft has revealed that two vulnerabilities in its Defender security software are being actively exploited. One is a privilege escalation flaw (CVE-2026-41091) that could allow an attacker to gain SYSTEM-level access, while the other is a denial-of-service flaw. Both are being used in real-world attacks.

Multiple vulnerabilities have been discovered in the Linux kernel, including a critical flaw known as 'Copy Fail'. This specific issue could allow a local attacker to gain higher privileges or escape from a container, potentially leading to a full system compromise. The update addresses these security risks.

A security researcher found a critical vulnerability on an official AMD website. AMD dismissed the report without a reward, stating the third-party software was out of scope, raising questions about corporate security responsibility.

A series of high-impact security incidents, including a mail server zero-day, poisoned npm packages, and a fake AI repository, highlight a dangerous trend. Attackers are exploiting single points of failure in software supply chains and cloud infrastructure to launch widespread, cascading attacks.

A vulnerability in Palo Alto Networks' GlobalProtect VPN is being actively exploited, allowing attackers to gain unauthorized access to corporate networks. Security firm Rapid7 reports that exploitation began just days after Palo Alto disclosed the issue, which was initially rated as medium-severity.

A critical vulnerability, dubbed 'Copy Fail,' has been discovered in the Linux kernel for Google Cloud Platform. The flaw allows local attackers to escalate privileges or escape containers. Several other security issues were also patched, which could have allowed system compromise. Users should update their systems immediately.

Ubuntu has patched several critical vulnerabilities in its QtSvg library. The flaws could allow an attacker to cause a denial of service or potentially execute arbitrary code by tricking an application into processing a malicious SVG image. The patches affect multiple Long-Term Support (LTS) versions.

Multiple vulnerabilities have been discovered in the Apache HTTP Server, including issues that could lead to denial-of-service, authentication bypass, and server-side request forgery. The flaws affect several Ubuntu LTS versions, prompting security updates for systems running the popular web server software.

Ubuntu 20.04 LTS systems are at risk due to critical flaws in their networking software. Attackers could exploit these vulnerabilities to run malicious code or cause a system crash, requiring immediate attention from security and IT teams.

Ubuntu has released a security update for its Long-Term Support versions to address a vulnerability in the Little CMS color management engine. The flaw could allow an attacker to cause a denial of service or potentially execute arbitrary code using a specially crafted ICC profile.

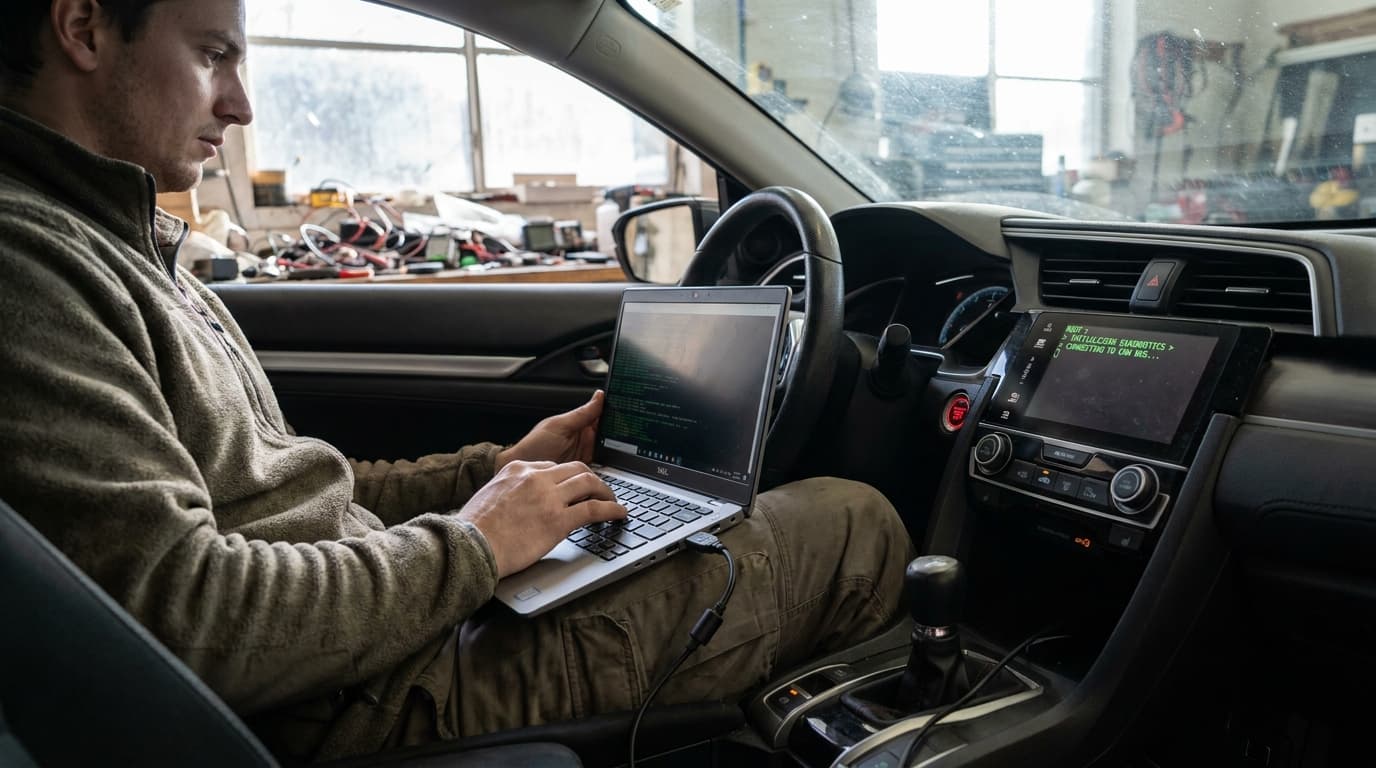
A security researcher found a major vulnerability in Honda Civics. An attacker with temporary physical access, like a valet, can gain control of the car's infotainment system, potentially accessing user data and vehicle functions.

A high-severity zero-day vulnerability in the KnowledgeDeliver Learning Management System was actively exploited by attackers. The flaw, caused by hard-coded keys, allowed them to install the Godzilla web shell and deploy Cobalt Strike for further network access. The vulnerability has since been patched.

A security vulnerability has been patched in Evolution Data Server for Ubuntu 18.04 and 20.04 LTS. The flaw could allow an attacker to delete arbitrary files on the system by exploiting how the server handles its local cache. Updating is recommended to protect system integrity.

Two vulnerabilities have been discovered in the Foomuuri firewall tool. The flaws allow a local, unprivileged attacker to bypass security measures and manipulate firewall configurations. The issues stem from improper authorization and validation within Foomuuri's D-Bus service, creating a significant privilege escalation risk.

A significant vulnerability has been found in the OverlayFS component of Ubuntu's Linux kernel, specifically affecting versions used on Google Cloud Platform. The flaw could allow a local attacker to bypass permission checks and gain elevated system privileges, posing a serious security risk for affected servers.

Two security vulnerabilities have been discovered in Luanti. The first (CVE-2026-40959) could allow an attacker to execute arbitrary code by bypassing sandbox restrictions. The second flaw could grant unintended access to insecure environments or the HTTP API, posing significant security risks to affected systems.

A security researcher found a critical flaw in AMD processors. After waiting 124 days for a patch, AMD reportedly denied the $10,000 bug bounty, raising concerns about its security response process.

A clickjacking vulnerability was found in the Transmission BitTorrent client's web interface. Attackers can use it to trick users into performing unintended actions on servers running the software, such as changing settings or deleting data.

A security vulnerability has been discovered in libssh2, a popular library for the SSH2 protocol. The flaw relates to how the library handles username and password lengths during authentication. A remote attacker could exploit this issue to trigger a denial-of-service, potentially crashing affected applications.

A denial-of-service vulnerability was found in the Qt Declarative module. Attackers can exploit improperly validated image attributes in Qt Quick's Text component to trigger excessive resource consumption, causing applications to crash. This affects developers using the cross-platform framework and requires patching.

A stored cross-site scripting (XSS) vulnerability has been found in Appsmith's SQL query editor. Attackers with developer access to a shared PostgreSQL database can inject malicious code by creating specially named database objects. This code executes when the autocomplete feature is used by other users.

Ubuntu has released a security update for EditorConfig across multiple long-term support versions. The patch fixes a vulnerability that could allow a local attacker to crash the application with a crafted configuration file, causing a denial of service. Users should update their systems.

Two denial-of-service vulnerabilities have been found in Libgcrypt, a common cryptographic library. Attackers can exploit flaws in how the library handles certain data for ECDH and Dilithium operations, potentially causing applications that rely on it to crash and become unavailable. Patches are recommended.

A denial-of-service vulnerability was found in pip, the Python package manager. The flaw, related to how its urllib3 library handles compressed data, could allow an attacker to crash development environments and CI/CD pipelines by consuming excessive resources. Ubuntu has released a patch to fix the issue.

A critical path traversal vulnerability has been found in the `tar-fs` Node.js library on Ubuntu 22.04 LTS and 24.04 LTS. The flaw allows attackers to write or overwrite files outside the intended directory using a specially crafted tar archive, posing a significant security risk.

A security vulnerability has been found in the Exim mail transfer agent. The issue, caused by improper memory handling when the PROXY protocol is enabled, could allow a remote attacker to access sensitive information before SMTP authentication. The flaw affects systems where this specific configuration is used.

A security vulnerability has been discovered in LibreOffice, a popular open-source office suite. Specially crafted OOXML documents with mismatched encryption parameters can cause the application to crash, leading to a denial of service, and could potentially allow an attacker to execute arbitrary code on a user's system.

Two high-severity vulnerabilities (CVSS 7.8) have been found in the popular Notepad++ code editor. The flaws, affecting versions up to 8.9.6, allow local attackers to execute arbitrary code on Windows systems by manipulating XML configuration files. Users are urged to update to the latest version.

A critical vulnerability has been patched in the `sed` utility on Ubuntu 18.04 LTS and 20.04 LTS. The flaw allowed a local attacker to overwrite arbitrary files by exploiting how `sed` handles symbolic links during in-place edits, potentially leading to privilege escalation on affected systems.

A critical vulnerability in the Everest Forms Pro WordPress plugin is being actively exploited by hackers. The flaw allows attackers to execute code remotely and completely take over websites running versions up to 1.9.12.

A security vulnerability has been found in Memcached's SASL authentication process. The flaw, a timing side channel, allows a remote attacker to analyze response times to potentially extract sensitive information like usernames and passwords, posing a risk to systems using this authentication method.

A vulnerability has been found in Dnsmasq, a common network service for DNS and DHCP. When configured with a specific option, mishandled BOOTREPLY packets can allow a remote attacker to crash the service, causing a denial of service, or potentially execute arbitrary code on the system.

A vulnerability in the ngtcp2 library, used for QUIC/HTTP/3, could allow remote code execution. The flaw involves writing data to a fixed-size buffer without checks. Exploitation requires a non-standard logging configuration (qlog) to be enabled, which reduces the immediate risk for most users.

Ubuntu has released a security update for a high-impact denial-of-service (DoS) vulnerability in Protocol Buffers. The flaw affects the Python library on Ubuntu 18.04 and 20.04 LTS, allowing attackers to crash applications and disrupt services by consuming excessive resources.