Hackers Stole Data From 1,000 Zyxel Switches
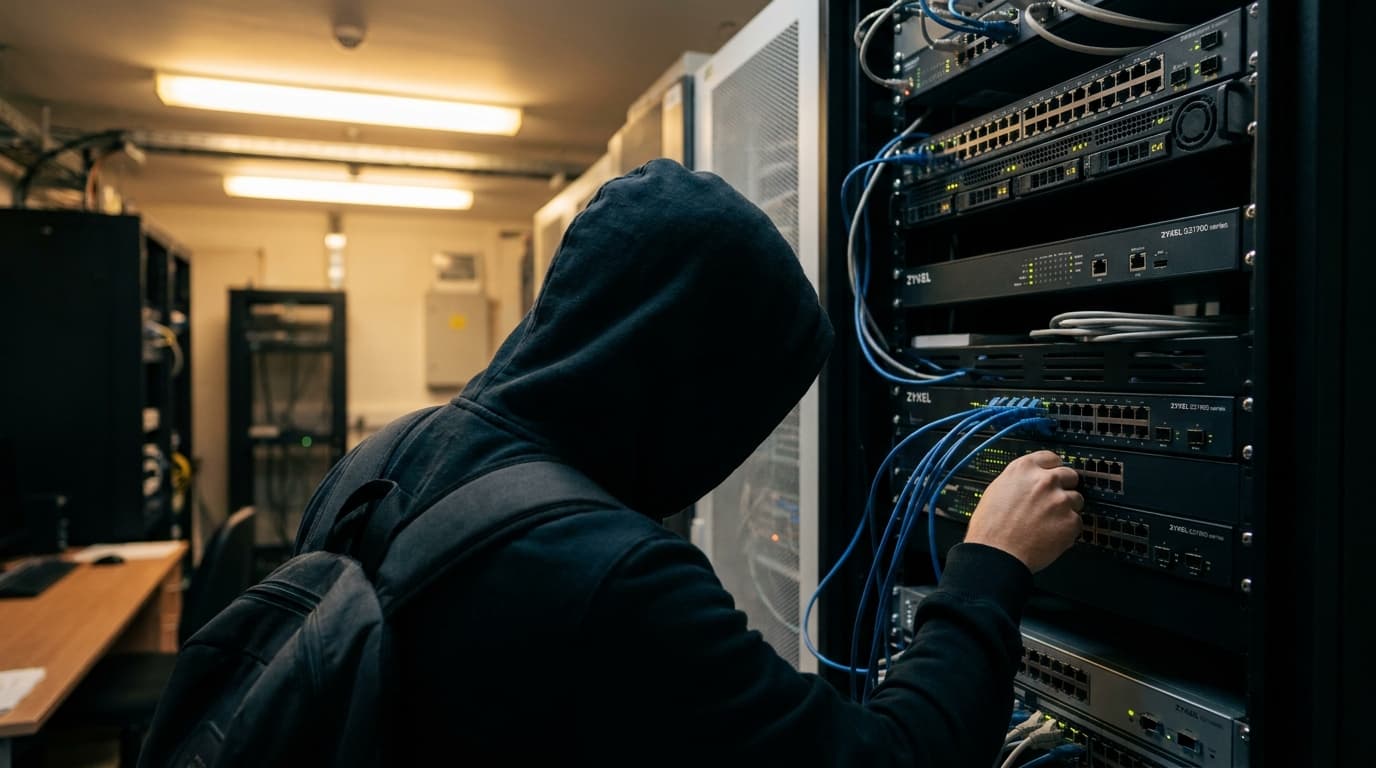
TL;DR: Zyxel has patched a critical zero-day vulnerability in its popular GS1900 series network switches. Attackers were actively exploiting the flaw to steal configuration files and credentials from nearly 1,000 devices before the fix was released.
Key facts
- Category
- Cybersecurity
- Impact
- Critical
- Published
- Source
- BleepingComputer
Full summary
Zyxel patched a zero-day flaw in its GS1900 network switches that hackers used to steal credentials from nearly 1,000 devices.
Zyxel has released a critical security patch for a zero-day vulnerability in its popular GS1900 series of network switches. According to reporting from BleepingComputer, the flaw was actively exploited by attackers before a fix was available. The campaign compromised nearly 1,000 devices globally, with attackers successfully exfiltrating sensitive configuration files and administrator credentials. The GS1900 series switches are widely deployed in small and medium-sized businesses, making this a significant threat for a large number of organizations. The vulnerability allowed unauthenticated attackers to gain access to the devices, highlighting the immediate need for IT and security teams to apply the newly released firmware update to protect their networks from takeover.
The vulnerability appears to have allowed attackers to bypass authentication on the switch's web-based management interface. While specific technical details of the exploit have not been fully disclosed, the impact suggests a command injection or remote code execution flaw. This means an attacker could send a specially crafted request to a vulnerable switch and trick it into running malicious commands. Once they gained this initial access, they could download the device's entire configuration file. This file is a treasure trove of sensitive information, often containing usernames, hashed passwords, network topology details, and other secrets that can be used to expand an attack across the entire corporate network.
This incident is part of a broader, concerning trend of attackers targeting network infrastructure devices. Hardware like switches, routers, and firewalls are often considered the “keys to the kingdom” by security professionals. Because they sit at the heart of the network, a single compromised device can provide a powerful foothold for attackers to monitor traffic, pivot to other internal systems, and maintain persistent, undetected access. Many of these devices are installed and then forgotten, rarely receiving the same level of patching and monitoring as servers or workstations. This “set-and-forget” mentality creates a massive, vulnerable attack surface that automated scanning tools can quickly identify and exploit on a global scale, as seen in similar attacks against hardware from Cisco, Fortinet, and other major vendors.
The most urgent takeaway for any organization using Zyxel GS1900 switches is to patch immediately. This event, however, serves as a crucial reminder of the importance of fundamental security hygiene for all network hardware. Teams must maintain a complete and accurate inventory of all devices on their network, as you cannot protect what you do not know exists. Implementing a robust patch management program that includes network infrastructure is non-negotiable. Looking forward, organizations should also evaluate their network architecture. Implementing network segmentation can help contain the damage if a core device is compromised, preventing attackers from moving freely across the entire environment. As attackers continue to focus on these often-neglected devices, proactive management is the only effective defense.
Why it matters
This zero-day affects widely used network hardware, the backbone of many small and medium-sized business networks. An unpatched switch provides a direct entry point for attackers to move laterally, steal credentials, and compromise the entire network, making immediate patching a critical security priority for all IT teams.
Business impact
Compromised network switches can lead to significant business disruption, data breaches, and financial loss. Attackers can steal sensitive company data, intellectual property, and customer information, leading to regulatory fines, reputational damage, and the high cost of incident response and recovery.
⚡ Action needed
Zyxel has released firmware updates for the affected GS1900 series switches. Administrators should identify vulnerable devices and apply the patch immediately to prevent exploitation.
Action checklist
- 1Identify all Zyxel GS1900 series switches on your network.
- 2Check the current firmware version against Zyxel's security advisory.
- 3Download and install the latest patched firmware (version 2.70(AAAA.7)C0 or newer).
- 4Review device logs for any signs of unauthorized access or configuration changes.
Tags
Related on Notifire
Related stories
Primary source: BleepingComputer