OpenAI Explains Why Your AI Agents Really Fail
TL;DR: AI agents fail for reasons beyond just model hallucinations. An OpenAI expert shared a framework for building reliable 'agent harnesses' that control state, scope authority, and validate actions to prevent common production errors.
Key facts
- Category
- AI
- Impact
- High
- Published
- Source
- InfoQ
Full summary
An OpenAI expert explains why production AI agents fail beyond just hallucinations, offering a new framework for building more reliable systems.
OpenAI expert Vinoth Govindarajan, in a presentation covered by InfoQ, outlined a critical framework for building reliable AI agents. He argued that the most common production failures aren't caused by model hallucinations, but by a lack of engineering discipline in the systems that control them. Govindarajan introduced the concept of an "agent harness," a control plane designed to manage an AI agent's actions and state. This structure provides the necessary guardrails to make autonomous agents predictable and safe enough for real-world applications. The core insight is that the intelligence of the AI model is only one part of the equation; the surrounding architecture is what ultimately determines its success or failure in a production environment, shifting the conversation from tweaking prompts to focusing on robust system design.
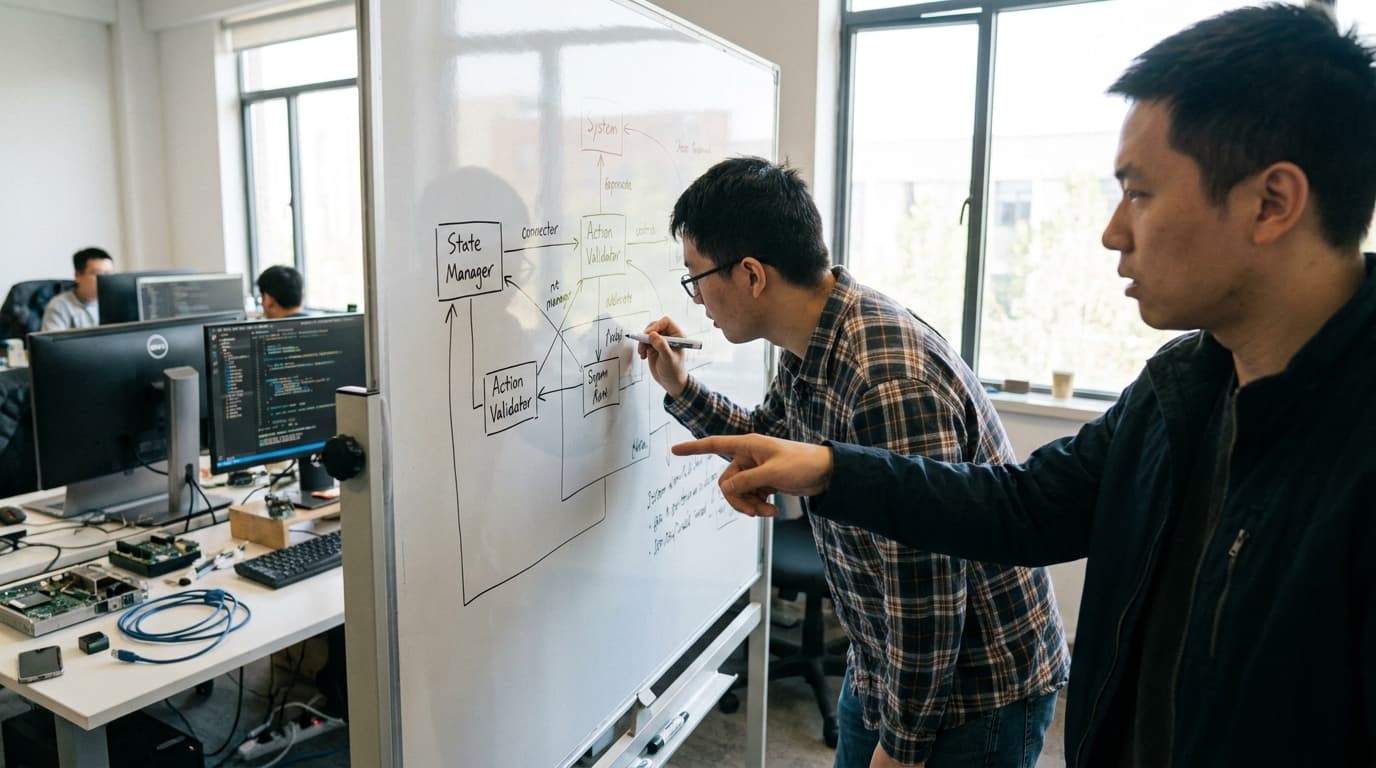
The agent harness operates on four key engineering principles. The first is establishing explicit state ownership, which means clearly defining what component is responsible for a piece of data at any given time to prevent conflicts and race conditions. Second is serializing concurrent state mutations, ensuring that if multiple processes try to change something simultaneously, the changes are applied in a predictable, orderly sequence. The third principle is scoping execution authority, which applies the principle of least privilege by strictly limiting what tools and actions an agent can access. Finally, the framework calls for validating actions at the user-visible edge, meaning that before an agent’s proposed action is executed, a final, deterministic check confirms it is valid, safe, and makes sense within the application's context.
This approach reflects a growing maturity in the field of AI engineering. For years, the focus has been on improving the capabilities of large language models themselves. However, as companies rush to deploy AI agents, they are discovering that a powerful model is not enough. The non-deterministic nature of AI requires a new layer of control, borrowing heavily from established software engineering and DevOps practices. Concepts like control planes, state management, and security sandboxing are not new, but their application to autonomous AI agents is a critical evolution. Govindarajan's framework formalizes what many advanced teams have been building through trial and error, providing a common language and set of best practices for the industry. It signals a move away from treating AI as a magical black box and toward integrating it as a component within a rigorously engineered system.
For founders, developers, and CTOs, the key takeaway is to invest as much in the agent's "harness" as in the agent's "brain." Simply plugging a powerful LLM into a set of tools is a recipe for unreliable and risky production systems. The path to successful AI products lies in disciplined system architecture that constrains and directs the model's power. Teams should begin evaluating their own AI agent projects against these principles, asking whether they have clear state ownership, proper authority scoping, and robust validation checks. Looking ahead, we can expect to see the emergence of more platforms and open-source tools that provide these harness capabilities out of the box, making it easier for all developers to build production-grade AI agents that users can trust.
Why it matters
For developers and CTOs, this provides a crucial engineering framework beyond prompt engineering. As AI agents move from experiments to production systems, their reliability becomes a critical bottleneck. These principles offer a structured approach to de-risk agent deployment and prevent unpredictable, costly failures in live environments.
Business impact
Companies investing in AI agents face significant operational and reputational risks from unpredictable failures. Adopting a structured 'agent harness' reduces the chance of costly errors, builds user trust, and accelerates the timeline for deploying autonomous AI systems that can create real business value.
Tags
Related on Notifire
Related stories
Primary source: InfoQ