Short, verified tech briefings on AI, Cybersecurity, Infrastructure, Database, and Tech Updates — with the analysis and action steps engineering teams need.
AI is creating new senior roles like 'forward deployed engineers' who act as generalists between models and customers. This shift suggests that traditional entry-level and specialized software development career paths are fundamentally changing.
Google is ending workarounds used by popular ad blockers like uBlock Origin in its Chrome browser. The change, part of the Manifest V3 transition, means many content-blocking extensions will become significantly less effective on Chrome, Edge, and Opera.
Ohio, a major hub for data center construction, has suspended a critical tax break program. The decision comes as the state re-evaluates the financial impact of energy-intensive AI data centers on its budget, signaling a potential shift in how states approach tech infrastructure incentives.
New data centers and crypto sites in Texas are failing key reliability tests. This puts the state's power grid at risk of outages this summer, threatening any business that relies on infrastructure in the major tech hub.
Spanish National Police arrested an individual accused of leaking sensitive data from multiple government organizations. The compromised information included personal details of employees at Spain's National Cybersecurity Institute (INCIBE), highlighting a significant breach of state security and privacy.
The ShinyHunters gang stole data from 137,000 school staff accounts by targeting the Infinite Campus K-12 system. The breach highlights the security risks of third-party platforms, as Salesforce was the point of entry.
An Iranian state-sponsored group, Nimbus Manticore, is running a new cyber campaign. They are using phishing and SEO poisoning to deploy malware called MiniFast and MiniJunk V2. The campaign targets aviation and software companies in the U.S., Europe, and the Middle East.
The SEC now requires public companies to disclose their cybersecurity strategies, risks, and governance in annual 10-K filings. An analysis of the first wave of these reports from top S&P companies reveals how industry leaders are approaching and communicating their security posture.
Oracle has set opposing policies for its open-source projects. OpenJDK now bans AI-generated code contributions, while GraalVM allows them, creating confusion for developers working under the same contributor agreement.
A security vulnerability has been discovered in LibreOffice, a popular open-source office suite. Specially crafted OOXML documents with mismatched encryption parameters can cause the application to crash, leading to a denial of service, and could potentially allow an attacker to execute arbitrary code on a user's system.
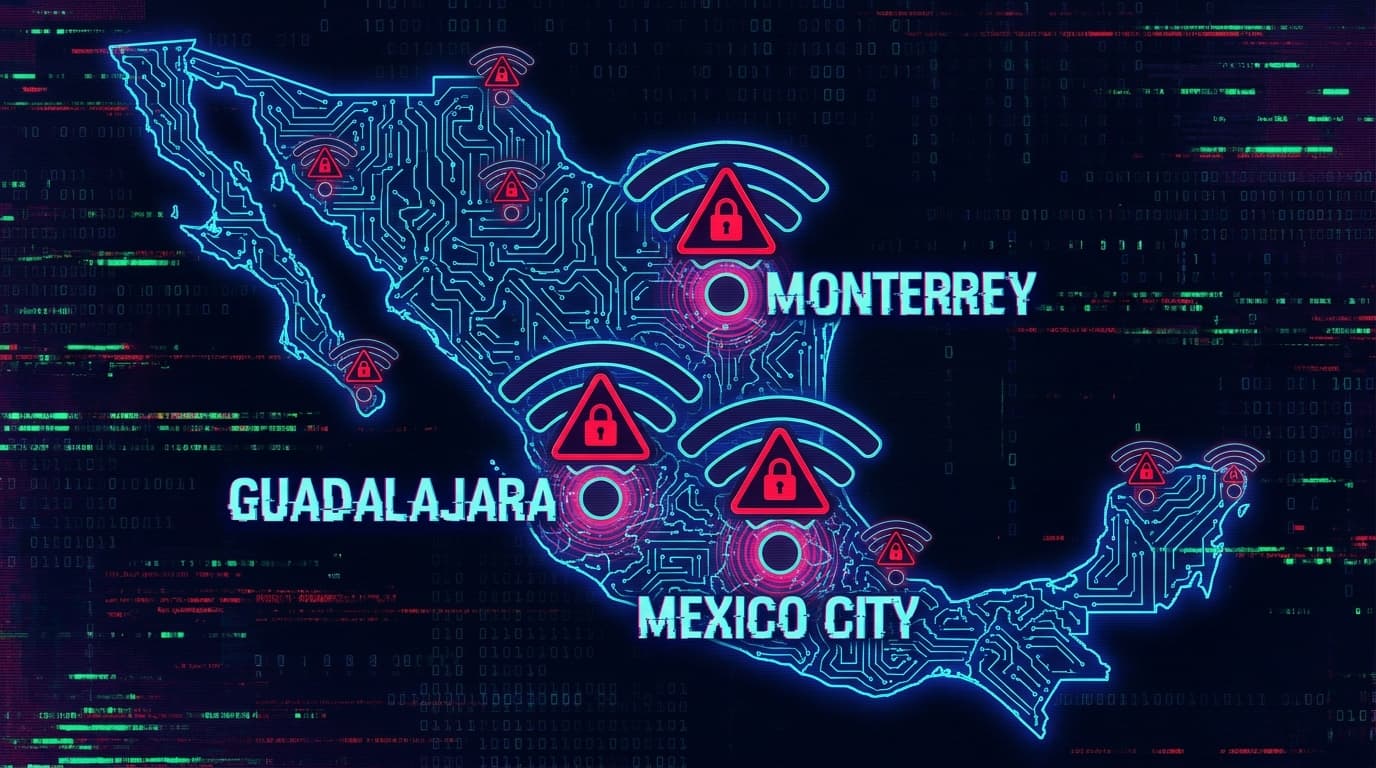
A Kaspersky security assessment of public Wi-Fi in Mexico's 2026 World Cup host cities—Mexico City, Monterrey, and Guadalajara—found significant security risks. The research highlights the dangers of unencrypted and poorly configured networks, posing a threat to international visitors and traveling employees.
Snowflake has launched CoCo, a new AI coding assistant for developers. The tool aims to provide a single, governed platform for building AI applications, simplifying the process for enterprises using Snowflake's data cloud.
DeepSeek is making a 75% price reduction on its flagship AI model permanent. This move intensifies the ongoing price competition among major AI providers, making powerful models more accessible and forcing competitors to re-evaluate their pricing strategies for developers and businesses.
A new technique called adaptive hedging significantly reduces high-percentile (p99) latency in complex microservice systems. It works by intelligently re-issuing requests that are predicted to be slow, cutting latency by up to 74%. The system uses real-time monitoring and a budget to avoid overwhelming services.
Robinhood has launched a new feature allowing users to create dedicated, funded accounts for AI agents. These agents can autonomously buy and sell stocks, enabling automated investment strategies like monitoring and trading within specific industries. The move opens new possibilities for algorithmic trading on the platform.
A new analysis of a popular underground hacking tutorial reveals the modern attacker's playbook. It shows a systematic workflow for finding and exploiting gaps in vulnerability management programs, offering defenders crucial intelligence on how threat actors operate and what they target first.
The European Union is exploring new regulations for smart glasses, citing major privacy concerns. This move could force tech companies to redesign products and rethink data handling, echoing the global impact of GDPR on the industry.
A new type of AI security threat is emerging as attackers move beyond simple jailbreaks. They are now exploiting the pre-defined 'personalities' of chatbots, manipulating their intended character traits to bypass safety controls and generate harmful content. This marks a significant evolution in LLM vulnerabilities.
The White House has proposed new rules that would give political appointees final approval over federally funded research grants. This change could shift funding decisions away from scientific merit review panels, potentially introducing political considerations into the process and impacting the direction of US innovation.
Ubuntu has patched several high-severity Linux kernel vulnerabilities affecting the NVIDIA Tegra IGX platform. The most critical flaw, known as "Copy Fail," could allow a local attacker to escalate privileges or escape a container, posing a significant risk for industrial and edge AI systems.
Data security firm Varonis is integrating with Anthropic's Claude Compliance API to enhance its Atlas platform. The partnership aims to provide businesses with better AI governance, allowing them to monitor how AI models interact with sensitive enterprise data, investigate potential risks, and maintain regulatory compliance.
A security vulnerability has been found in the Exim mail transfer agent. The issue, caused by improper memory handling when the PROXY protocol is enabled, could allow a remote attacker to access sensitive information before SMTP authentication. The flaw affects systems where this specific configuration is used.
Researchers uncovered 152 Chrome wallpaper extensions with over 105,000 installs that secretly distribute adware. The extensions generate fake web traffic and display unwanted ads, posing a security risk to users and corporate networks.
As AI agents increasingly write code, the key challenge is trust. For cloud-native apps, this means verifying an agent's work in a live runtime environment before it ever becomes a pull request, ensuring the code is safe and effective.