Short, verified tech briefings on AI, Cybersecurity, Infrastructure, Database, and Tech Updates — with the analysis and action steps engineering teams need.
Microsoft is warning of a new campaign where attackers use AI chatbot recommendations to lead users to malicious websites. This social engineering tactic distributes cryptojacking malware by exploiting user trust in AI-generated suggestions, extending threats beyond conventional search engine results.
Microsoft is advocating for Coordinated Vulnerability Disclosure, urging researchers to report issues privately. The statement follows a public dispute where a security researcher disclosed multiple zero-day vulnerabilities, leading to a debate on platform governance and responsible disclosure ethics.
Charter Communications, a major US telecom, was hacked by the ShinyHunters extortion gang in early April. The breach exposed personal information from nearly 4.9 million accounts. The incident was reported by the data breach notification service Have I Been Pwned, highlighting a significant security failure.
A developer embedded a malicious prompt into the open-source library `jqwik`. The hidden instruction tricks AI coding assistants into deleting application output files. This novel supply chain attack highlights new security risks for developers who rely on AI tools for coding and debugging tasks.
The FBI reports Americans lost nearly $900 million to AI-powered scams. The figure, likely an underestimate, highlights a rapidly growing threat for businesses driven by voice cloning and deepfakes.
A critical vulnerability in the WP Maps Pro WordPress plugin is being actively exploited by attackers. The flaw allows unauthorized users to create new administrator accounts, granting them full control over affected websites. The plugin has over 15,000 sales, indicating a significant number of potentially vulnerable sites.
A key security feature is broken in Haskell's core TLS libraries. This flaw allows attackers to potentially impersonate trusted servers, creating a risk of man-in-the-middle attacks for applications built with the language.
A critical SQL injection vulnerability (CVE-2026-26980) in the popular Ghost CMS is being actively exploited. Attackers are injecting malicious JavaScript into sites to conduct 'ClickFix' attacks. The flaw, rated 9.4 on the CVSS scale, allows unauthenticated attackers to read arbitrary data from the database.
An INTERPOL-led operation shut down Sniper Dz, a phishing service that operated for a decade. The takedown, involving 13 countries, disrupts a major tool used by cybercriminals to launch attacks against businesses and individuals.
A security researcher is threatening to publicly release another zero-day exploit for Microsoft Windows, escalating a dispute with the company. The threat puts pressure on Microsoft and creates a potential security risk for all Windows users, pending the company's response or the exploit's public disclosure.
CISA has added a high-severity Oracle WebLogic Server vulnerability, CVE-2024-21182, to its Known Exploited Vulnerabilities catalog. The flaw allows unauthenticated attackers with network access to take control of affected servers. Evidence confirms that this vulnerability is being actively exploited in the wild, requiring immediate attention.
A vulnerability in the popular Kea DHCP server allows a remote attacker to crash it with a specially crafted message. This can cause a denial of service, potentially disrupting network access for all connected devices.
Many teams know their software supply chain is a risk, but struggle to implement security. These five key practices, from scanning dependencies to using a Software Bill of Materials (SBOM), help secure your development pipeline.
Deepfakes are evolving from public misinformation tools into a significant corporate security risk. Attackers use synthetic media to impersonate executives and manipulate business processes like payment approvals. A Gartner report indicates that 62% of organizations have already been affected by this growing threat.
A North Korean hacking group is targeting developers with fake job offers and code review requests. The sophisticated phishing campaigns aim to trick technical staff into installing malware, posing a direct threat to company security.
The FBI is warning that crypto scammers are now using physical couriers to collect cash from victims. This escalation of 'pig butchering' scams blends digital deception with real-world logistics, increasing the threat to individuals.
AI tools are dramatically reducing the time it takes to exploit software vulnerabilities. The window between a vulnerability's disclosure and widespread attacks has shrunk from days to mere hours. This trend forces security teams to adapt their strategies for managing and patching system weaknesses.
Google is introducing a new feature to detect fake calls that use AI deepfake technology. As scammers increasingly spoof trusted numbers and impersonate people, this tool aims to protect users from sophisticated social engineering attacks by identifying and flagging potential AI-generated voices during calls.
Multi-factor authentication (MFA) is being defeated by a simple tactic. Attackers with stolen credentials spam users with login approval requests, hoping to trick them into granting access out of confusion or fatigue. This method bypasses a core security protection without stealing the second factor.
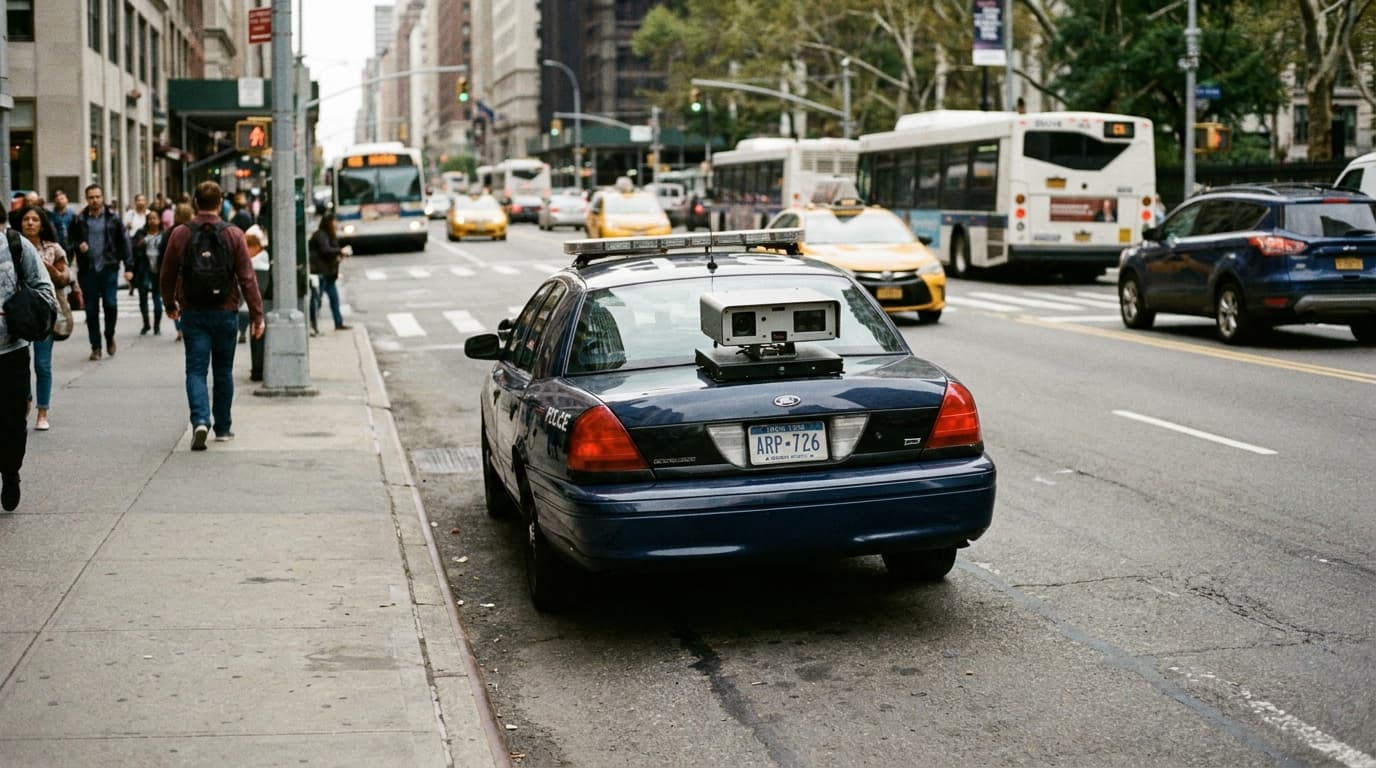
A surveillance firm is adding Bluetooth sensors to license plate readers. The new system will capture unique IDs from phones and wearables inside cars, linking vehicles directly to their occupants for law enforcement tracking.
A new Linux kernel security patch has been released to address several vulnerabilities. The update fixes critical flaws, including one that could allow for privilege escalation and another that could lead to a container escape, posing a significant risk to system integrity and data security.
While overall employment numbers remain stable, recent research from Stanford and Anthropic indicates a troubling trend: AI is weakening entry-level job opportunities. This shift threatens the career pipeline, making it harder for new talent to gain experience and advance.
Malicious actors are stealing encrypted data today, planning to break it once quantum computers are powerful enough. A recent survey shows many organizations are not preparing for this long-term "harvest now, decrypt later" security threat.
A new malvertising campaign on Google and YouTube is distributing a macOS backdoor called FlutterShell. The operation, codenamed FlutterBridge, is believed to be an evolution of a previous campaign by the same cybercrime group, targeting macOS users with sophisticated social engineering tactics.